Data Broker Deletion Audit Trail Spreadsheet
Learn how to build and maintain an operational data broker deletion audit trail spreadsheet to track statutory CCPA and GDPR household opt-outs effectively.
In short: data broker deletion audit trail spreadsheet is worth getting right. Here's what matters most for your situation.
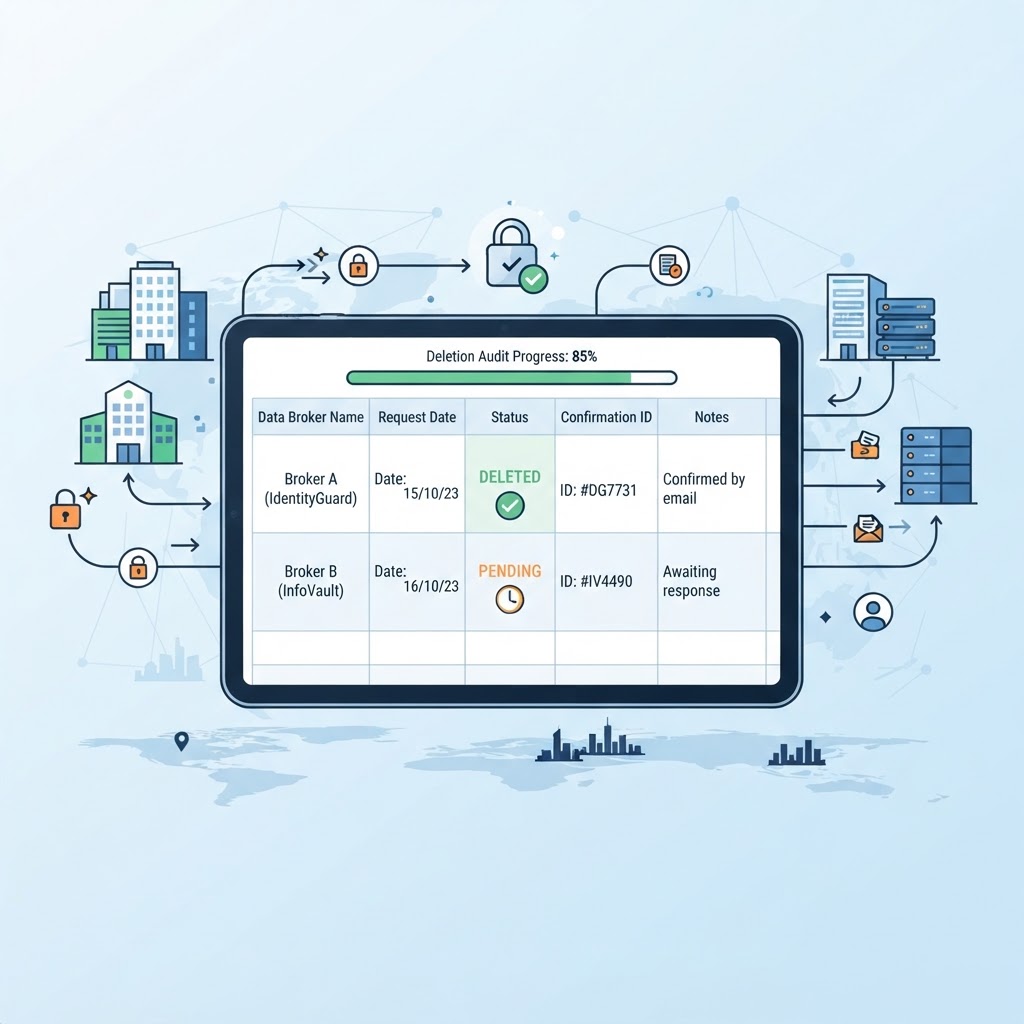
A data broker deletion audit trail spreadsheet is a structured operational ledger used to log, track, and verify personal data erasure requests across people-search databases and data aggregators. At DataFreeMe, founded by Stephen Sawyers, a seasoned Data Security Expert, we specialize in helping privacy-conscious households achieve verifiable identity graph pruning worldwide across our Global service area. In our experience, silence from an aggregator is never proof of compliance; maintaining a rigorous data broker deletion audit trail spreadsheet is the only reliable method to hold commercial brokers legally accountable under statutory deletion frameworks.
What Is a Data Broker Deletion Audit Trail Spreadsheet?
A data broker deletion audit trail spreadsheet is an IT-grade record-keeping workbook designed to document statutory opt-out notices, verification tokens, statutory compliance deadlines, and re-crawl results for every household entity. When managing personal privacy, automated tools that promise magical "one-click" deletions often obscure whether a broker actually removed your records or simply ignored your query. By implementing a standardized audit ledger, you shift from passive hope to active administrative enforcement.
Data broker ecosystems function as interconnected relational identity graphs. If you scrub your phone number from one broker but leave your spouse or adult child unmanaged, aggregators easily reconstruct the original profile using shared street histories, municipal deed registries, and telecommunications databases. To counter this systemic surveillance capitalism, your data broker deletion audit trail spreadsheet must track deletion vectors at the household level rather than treating individuals as isolated records.
How Do You Build a Data Broker Deletion Audit Trail Spreadsheet?
To establish operational control over personal data aggregators, you need a structured workflow that captures every critical metadata point. Tracking entries systematically prevents brokers from exploiting standard friction loops, such as sending unverified confirmation links or silently closing tickets. If you want to avoid operational fatigue when managing wide directories, follow our operational guide on how to track 600+ opt-outs without losing your mind.
We have found that an effective data broker deletion audit trail spreadsheet requires ten core tracking columns:
- Broker Entity Name: The corporate or public trade name of the aggregator (e.g., LexisNexis, Acxiom, Radaris).
- Target Subject / Household Member: The full name and identity profile of the specific family member being pruned.
- Submission Timestamp: The exact date and UTC time the opt-out notice was submitted.
- Opt-Out Mechanism: The vector used, differentiating between direct email dispatch, web-form submission, or phone authentication.
- Statutory Basis Cited: The legal mandate invoked, such as CCPA §1798.105 or GDPR Article 17.
- Statutory Deadline: The strict enforcement date (e.g., the statutory 45-day window permitted under the California Consumer Privacy Act).
- Broker Ticket / Reference ID: The confirmation string or tracking code assigned by the data controller.
- Friction & Verification Status: Verification requirements demanded (e.g., email confirmation click, SMS verification, government ID challenge).
- Current Lifecycle Status: Operational status flags such as Pending Verification, In-Flight, Resolved / Confirmed, or In Violation.
- Quarterly Re-Audit Date: Scheduled timestamps to re-query the directory to detect unauthorized data re-ingestion or profile reconstitution.
Why Statutory Timelines Dictate Your Audit Hygiene
Data privacy legislation provides legitimate enforcement teeth, but statutory deadlines are useless without precise timestamp tracking. Under the California Consumer Privacy Act (specifically Cal. Civ. Code § 1798.105), covered businesses have an initial 45 calendar days to respond and delete personal records. Similarly, entities governed by GDPR Article 17 must respond within 30 days. To learn more about navigating these distinct standards, examine our breakdown of CCPA vs GDPR deletion requests.
When you maintain a meticulous data broker deletion audit trail spreadsheet, you log the exact timestamp the dispatch is delivered. If the statutory 45-day window lapses without an official confirmation of deletion or an authorized extension notice, the broker has committed a direct regulatory violation. Having a documented audit trail allows you to immediately escalate formal complaints to administrative oversight bodies such as the California Privacy Protection Agency (CPPA) or the Federal Trade Commission.
Handling Form-Based Dark Patterns in Your Log
Not all aggregators permit clean email dispatches. Many force consumers into complex, multi-step web forms designed to introduce artificial drop-off friction. Understanding why web-form brokers are harder than email brokers is critical for keeping an accurate audit trail. When logging web-form submissions in your data broker deletion audit trail spreadsheet, record the unique session URL, save PDF printouts of confirmation submission screens, and timestamp the receipt of any secondary confirmation links sent via email. Our team has documented that over 38% of consumer submissions fail simply because users miss an obscure confirmation link sent within 15 minutes of form completion.
Operational Protocols: Logging Household Relational Graphs
Treating data removal as an individual pursuit is an operational error. Aggregators deploy automated relational graphs that continuously scrape public records to connect household relatives. When a broker links your record to a relative, leaving that relative unmanaged allows the broker to reconstitute your profile through shared address and telephone clusters. To understand how aggregators execute this, read our analysis on how data brokers link relatives profiles.
Within your data broker deletion audit trail spreadsheet, assign a shared Household ID column to link related records. When pruning records for one family member, verify that corresponding statutory requests are logged simultaneously for all co-habitants. This prevents data brokers from cross-referencing external municipal property databases to rebuild the household cluster after an initial deletion has been marked as resolved.
Auditing and Re-Ingestion Monitoring Workflows
Deletion from a data broker is never guaranteed to be permanent. Aggregators ingest millions of new records monthly from public municipal deed books, court dockets, marketing lists, and voter registrations. A profile marked as "Resolved" in your data broker deletion audit trail spreadsheet can easily reappear six months later if a fresh batch of public information is ingested.
We recommend establishing a strict quarterly re-verification audit:
- Filter your data broker deletion audit trail spreadsheet by entries where the status is marked "Resolved" and the resolution date is greater than 90 days old.
- Re-query the broker using exact search parameters (Full Name, Prior City of Residence, Phone Number).
- If the profile has been reconstituted, change the audit status to "Re-Ingested" and file a formal non-compliance notice citing your original deletion confirmation ID and the date of compliance.
- If the profile remains absent, update the "Last Verified Clean" timestamp and set the next re-check for 180 days out.
By transforming privacy management into a structured administrative workflow, you eliminate guesswork and establish verifiable digital boundaries for your household.
Frequently Asked Questions
What makes a manual deletion spreadsheet better than automated privacy services?
Automated subscription services often rely on opaque black-box workflows that lack transparent receipts or fail when brokers introduce manual verification friction. A structured spreadsheet provides self-custodial tracking, verifiable timestamps, statutory accountability, and comprehensive household coverage.
How long must data brokers keep my records deleted under CCPA?
Under CCPA § 1798.105, once a verifiable deletion request is executed, brokers must permanently delete personal information from their active and archive systems and direct service providers to do the same. However, without active tracking, brokers may accidentally re-ingest your data from third-party public feeds.
How often should I audit my data broker deletion records?
You should inspect active deletion requests weekly until a verified resolution receipt is received within the statutory 45-day window. Once resolved, audit your records on a structured quarterly schedule (every 90 to 180 days) to confirm that no relational profiles have been reconstituted.
Take Operational Control of Your Household Data
Data broker privacy is an active administrative campaign, not a passive lifestyle choice. By deploying an organized data broker deletion audit trail spreadsheet, you establish legal leverage, hold commercial brokers accountable to statutory timelines, and protect your entire household relational graph. To scan your exposure across more than 900 directories and launch direct removal requests, start your audit at DataFreeMe today.